CountryGCC overviewUnited Arab EmiratesSaudi ArabiaOmanQatar
SentraGuard · Shadow AI · State of Qatar

QCB expects a register of every AI system. Shadow AI never makes the list.

2-minute walkthrough · tap for sound · demo dataWatch with chapters

The QCB AI Guideline asks for a register of all AI systems and board accountability. 69% of workers in Qatar already use AI at work. SentraGuard finds every AI tool in use, governs it, and proves it to QCB and the NCSA.

Find your shadow AI on the day you deploy. Reach full shadow AI governance in one week.

69%of workers in Qatar used AI at work in the past year; 44% use generative AI weekly or daily. PwC Hopes and Fears 2025
QAR 5Mmaximum fine under the PDPPL, Law No. 13 of 2016
USD 150Kfirst QFC data protection fine, October 2024, partly for a late breach notice
2024QCB AI Guideline: AI register, prior approval, board accountability
Day 0shadow AI inventory on the day you deploy. Full governance by day 7
Trusted by regulated institutions
Top private bank, IndiaFortune 500 technology firmNational payments operatorMedia conglomerateGeneral insurerAI productivity platform
GCC channel
Value-added distributorForcespot
Value-added solution sellerNitronEdge
Memberships and partners DSCI member Coalition for Secure AI member OWASP GenAI Security Project Google Cloud partner ISO 27001 CERTIFIED
Why usage control

Shadow AI is a usage problem. Blocking apps does not solve it.

Sensitive data does not leave through files any more. It leaves in a prompt, a paste and an agent's tool call, usually on a personal account. Usage control decides what happens at that moment.

01

Personal accounts, outside SSO

67% of employees reach AI from non-corporate accounts on corporate devices. No log, no attribution, no answer for the auditor. Verizon DBIR 2026

02

Prompts and the clipboard, not uploads

Shadow AI is now the third most common non-malicious insider action in DLP data, with detections up 4x in a year. Source code is the top data type uploaded. Verizon DBIR 2026

03

Agents that act, not just answer

Coding agents and MCP servers call tools and write to data. A tool list cannot govern a tool call.

04

The AI register has a gap

The QCB AI Guideline asks banks to keep an up-to-date register of all AI systems and to disclose it to QCB each year. Tools staff open on personal accounts are AI systems in use. Without discovery, they never reach the register. QCB AI Guideline 2024

Legacy DLP sees file uploads only. SentraGuard reads the session: uploads, prompts, clipboard and agent calls. Employee PublicAI tool File upload Prompt text Clipboard paste Agent tool call Legacy DLPone lane not seen SentraGuardevery lane SGSGSGSG

The session blind spot

Qatar

What Qatar expects, and what SentraGuard hands over

QCB, the NCSA and the QFC each set rules that reach AI use at work. Here is what applies, and the evidence SentraGuard produces for each.

Banking

QCB Artificial Intelligence Guideline, September 2024

Banks must keep a register of all AI systems with annual disclosure, get QCB approval before launching an AI system and for high-risk AI outsourcing, keep a human oversight protocol, and tell customers when they deal with AI. The board is accountable. QCB also issued a Cloud Computing Regulation (2024) and a Data Handling and Protection Regulation (2025).

SentraGuard gives youAn AI register built from discovery, not a survey: every app, account, agent and MCP server, with owner, class and data seen.
Data protection

PDPPL, Law No. 13 of 2016

The NCSA regulates the law through its National Cyber Governance and Assurance Affairs. Fines reach QAR 1 million or QAR 5 million, depending on the article. Data of a special nature, such as health, religion and children's data, needs a permit. NCSA guidelines expect breach notice within 72 hours. In the QFC, the first data protection fine was USD 150,000.

SentraGuard gives youRedaction that keeps QIDs, IBANs and special-nature data out of public AI tools, with a timestamped decision log.
Cybersecurity

NCSA guidance on secure AI

The NCSA Guidelines for Secure Adoption and Usage of AI (February 2024) cover generative AI, privacy and governance. The National Information Assurance Standard and the National Data Classification Policy (2023) apply to government and vital sectors. The National Cyber Security Strategy runs from 2024 to 2030.

SentraGuard gives youControls mapped to NIA data levels, events streamed to your SIEM, and agents gated at the tool call.
AI policy and residency

National AI Strategy and Cloud First

Qatar's National AI Strategy dates from 2019. MCIT published Principles and Guidelines for Ethical AI in 2024. The Cloud First Policy classes government data from C0 to C4 and exempts C4, which stays under the national information assurance policy. The financial markets regulator QFMA proposed draft AI rules in 2025.

SentraGuard gives youA backend in your data centre in Qatar, air gapped for the most sensitive data classes.
Identifiers SentraGuard detects and redacts in QatarQatar ID, QID (11 digits)Qatar IBAN (QA, 29 characters)Card number (PAN)Special-nature dataCustomer PIISource code and secretsMNPI
Sources for the Qatar facts on this page
  1. QNA: QCB issues Artificial Intelligence Guideline
  2. Pinsent Masons: QCB AI guideline obligations
  3. QNA: QCB Cloud Computing Regulation
  4. Mondaq: QCB Data Handling and Protection Regulation
  5. PDPPL, Law No. 13 of 2016 (English text)
  6. DLA Piper: Qatar data protection
  7. The Peninsula: first QFC data protection fine
  8. The Peninsula: NCSA secure AI guidelines
  9. The Peninsula: National Data Classification Policy
  10. Government Communications Office: National Cyber Security Strategy 2024 to 2030
  11. MCIT Cloud First Policy
  12. Middle East Briefing: QFMA draft AI rules
  13. Regulations.ai: MCIT ethical AI principles
  14. PwC Hopes and Fears 2025: Qatar
  15. Microsoft Purview: Qatari ID number format

Checked 24 September 2026. Regulations change; confirm current text with your counsel.

Visibility

See every AI app, agent and account your workforce uses.

15%of users run unauthorised AI browser extensions. Verizon DBIR 2026
4surfaces reporting to one backend
2account types split: corporate, personal

One console for discovery, protection and proof

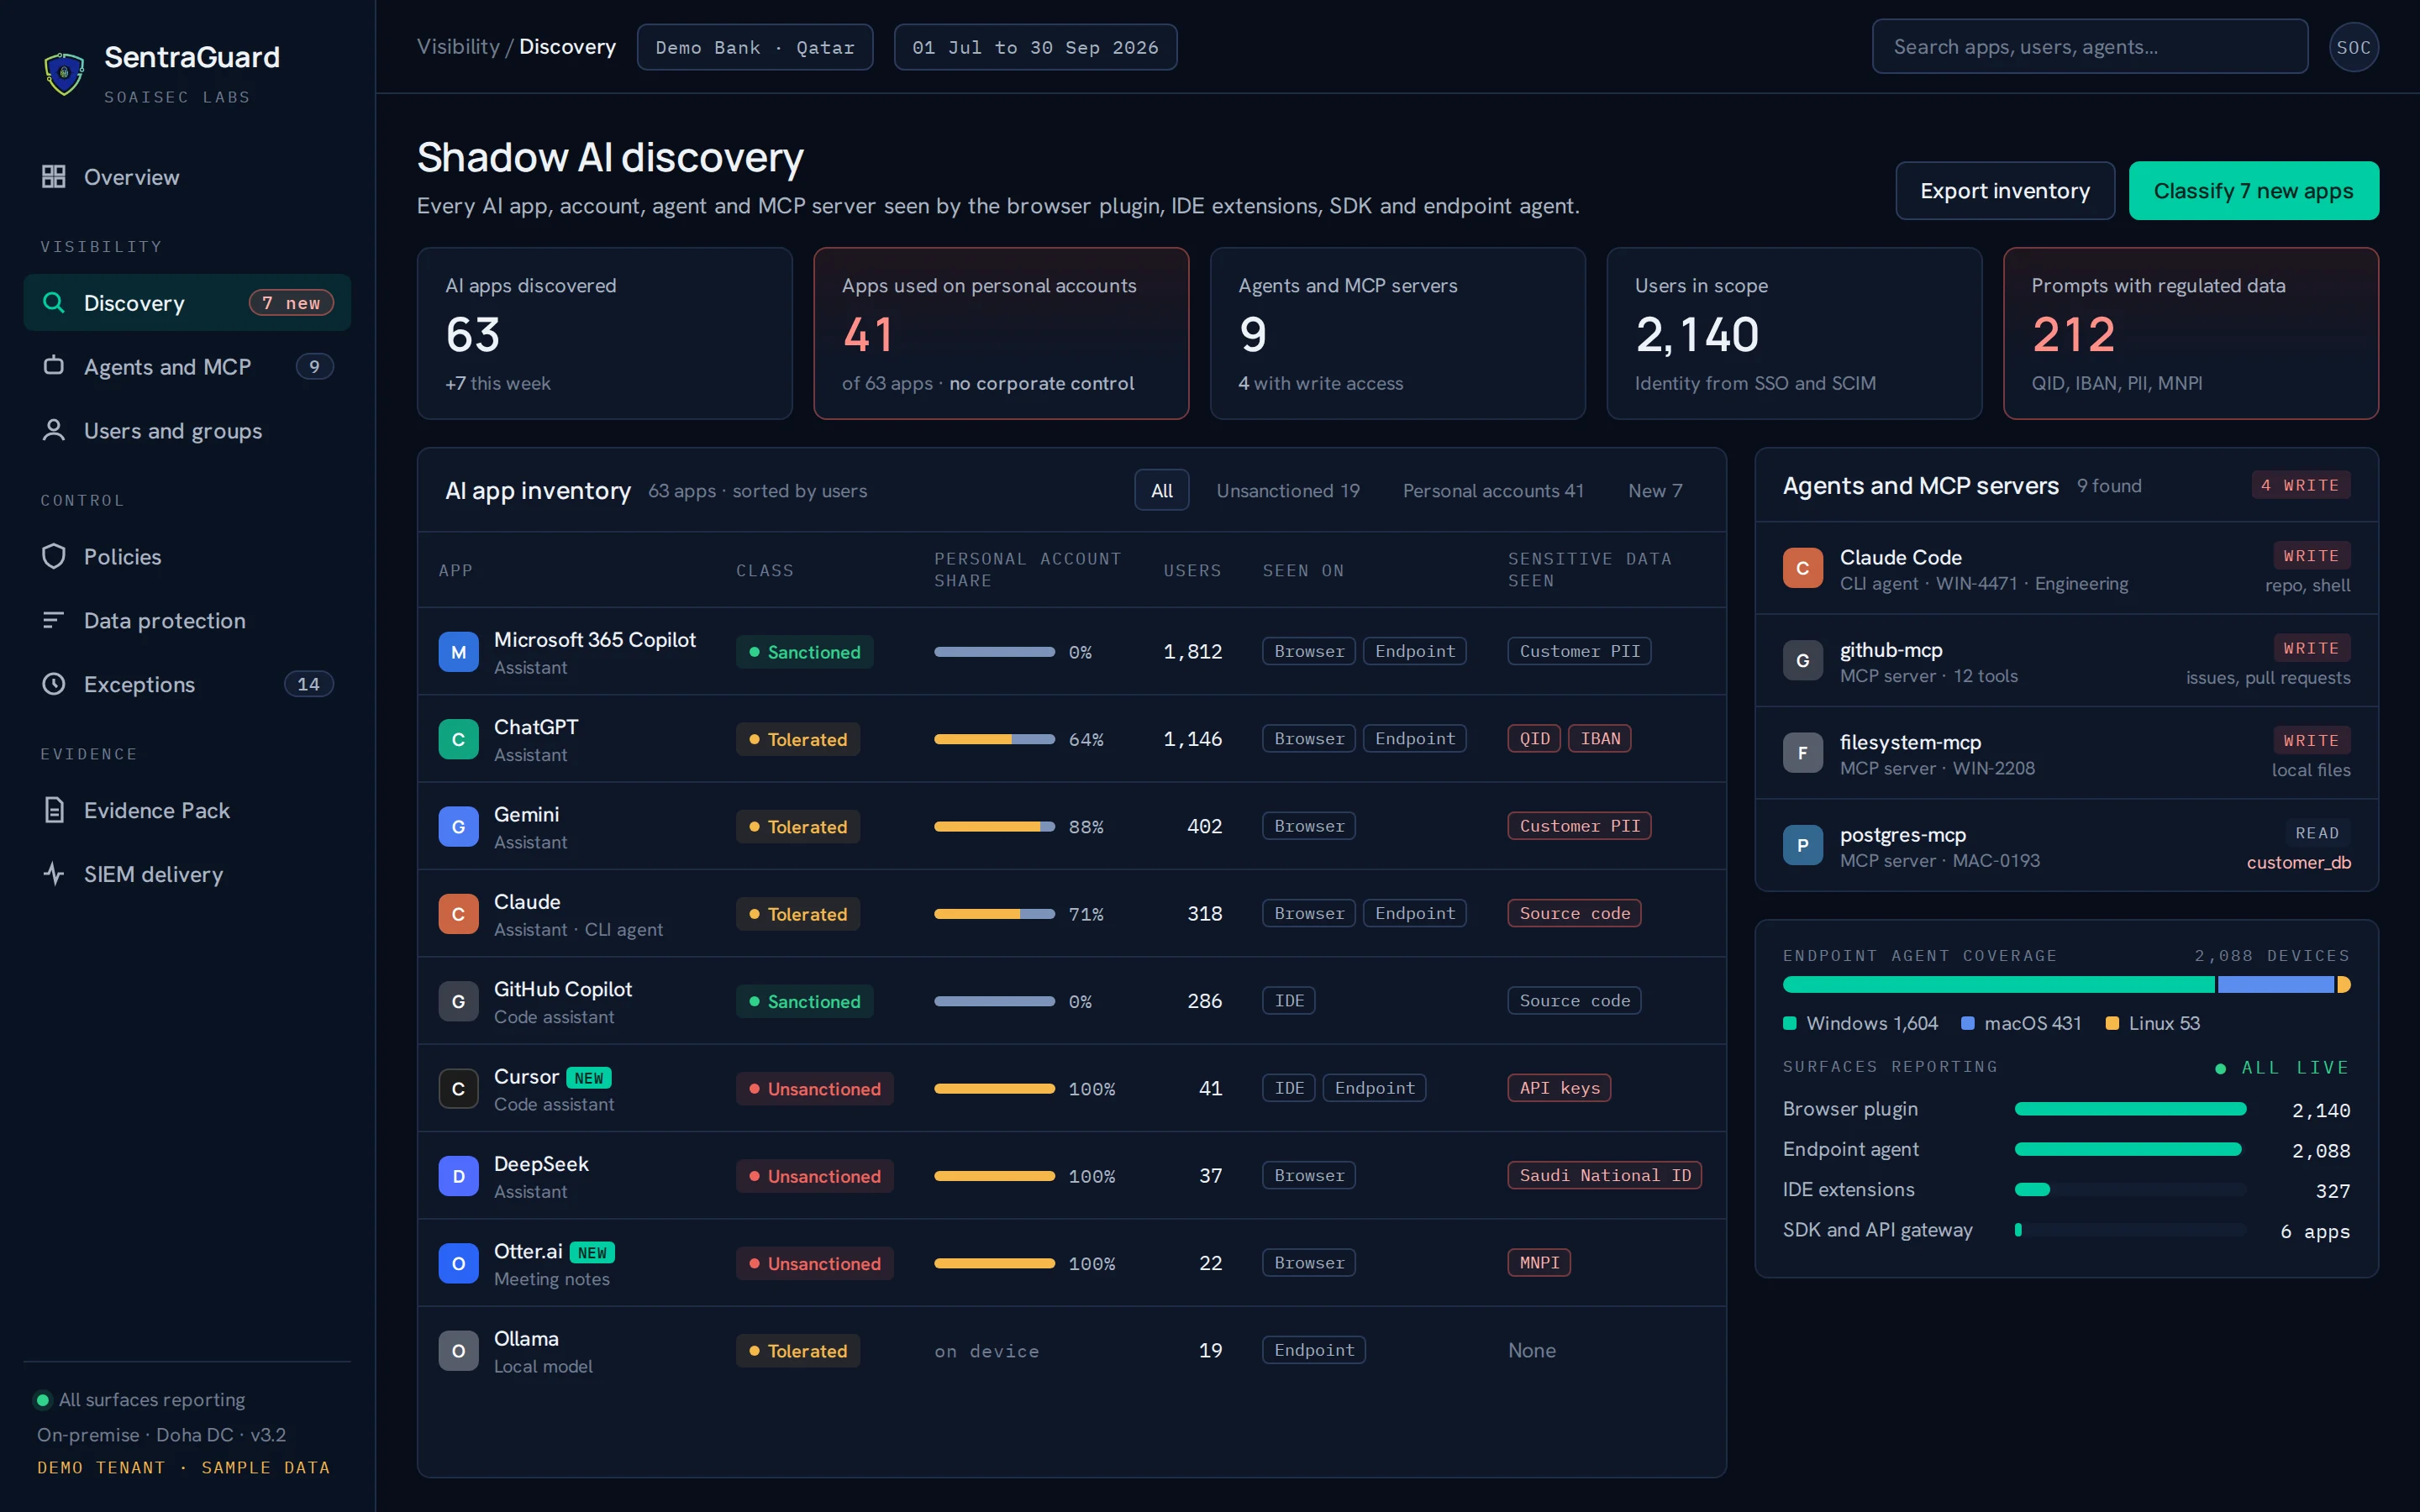
The browser plugin sees web apps and extensions. The IDE extension sees Cursor, VS Code and Copilot. The SDK and API gateway see your own apps. The endpoint agent runs on Windows, macOS and Linux and sees desktop AI apps, CLI agents, local models and MCP servers. Everything lands in one console.

  • Corporate versus personal account, per session
  • New tools detected by behaviour, not only by list
  • Agents and MCP servers with the tools and data they can reach
sentraguard console · demo tenant
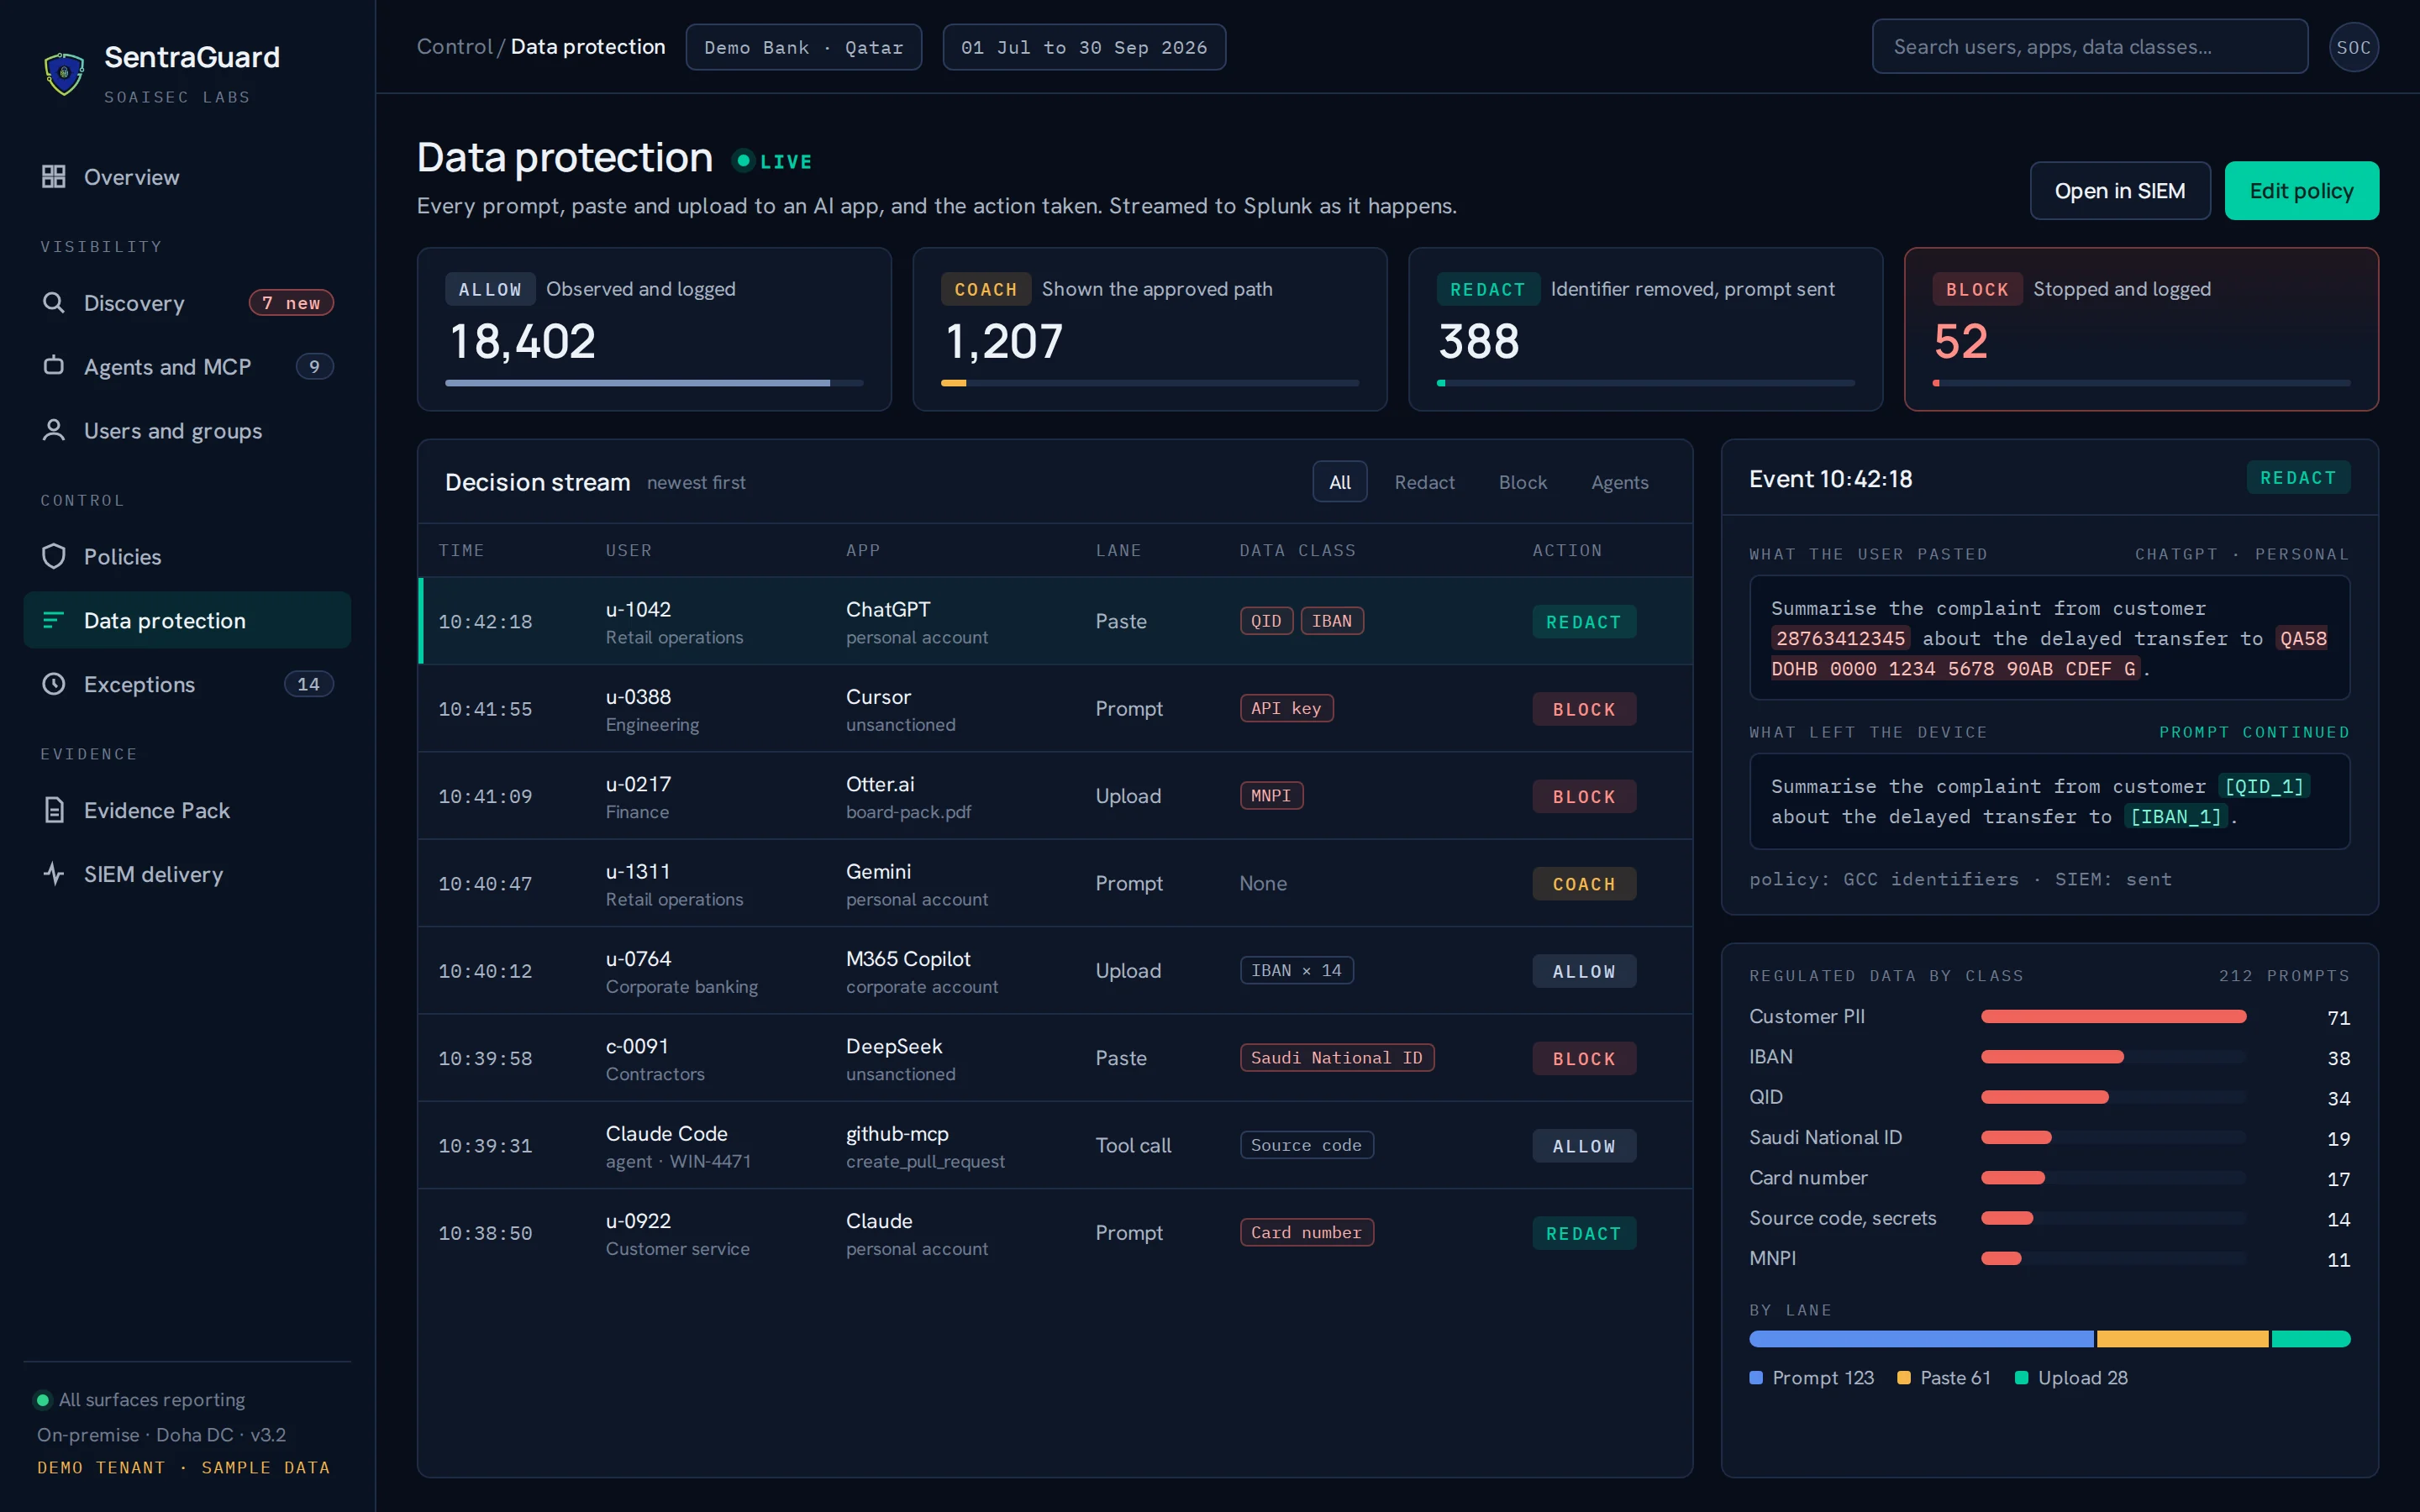
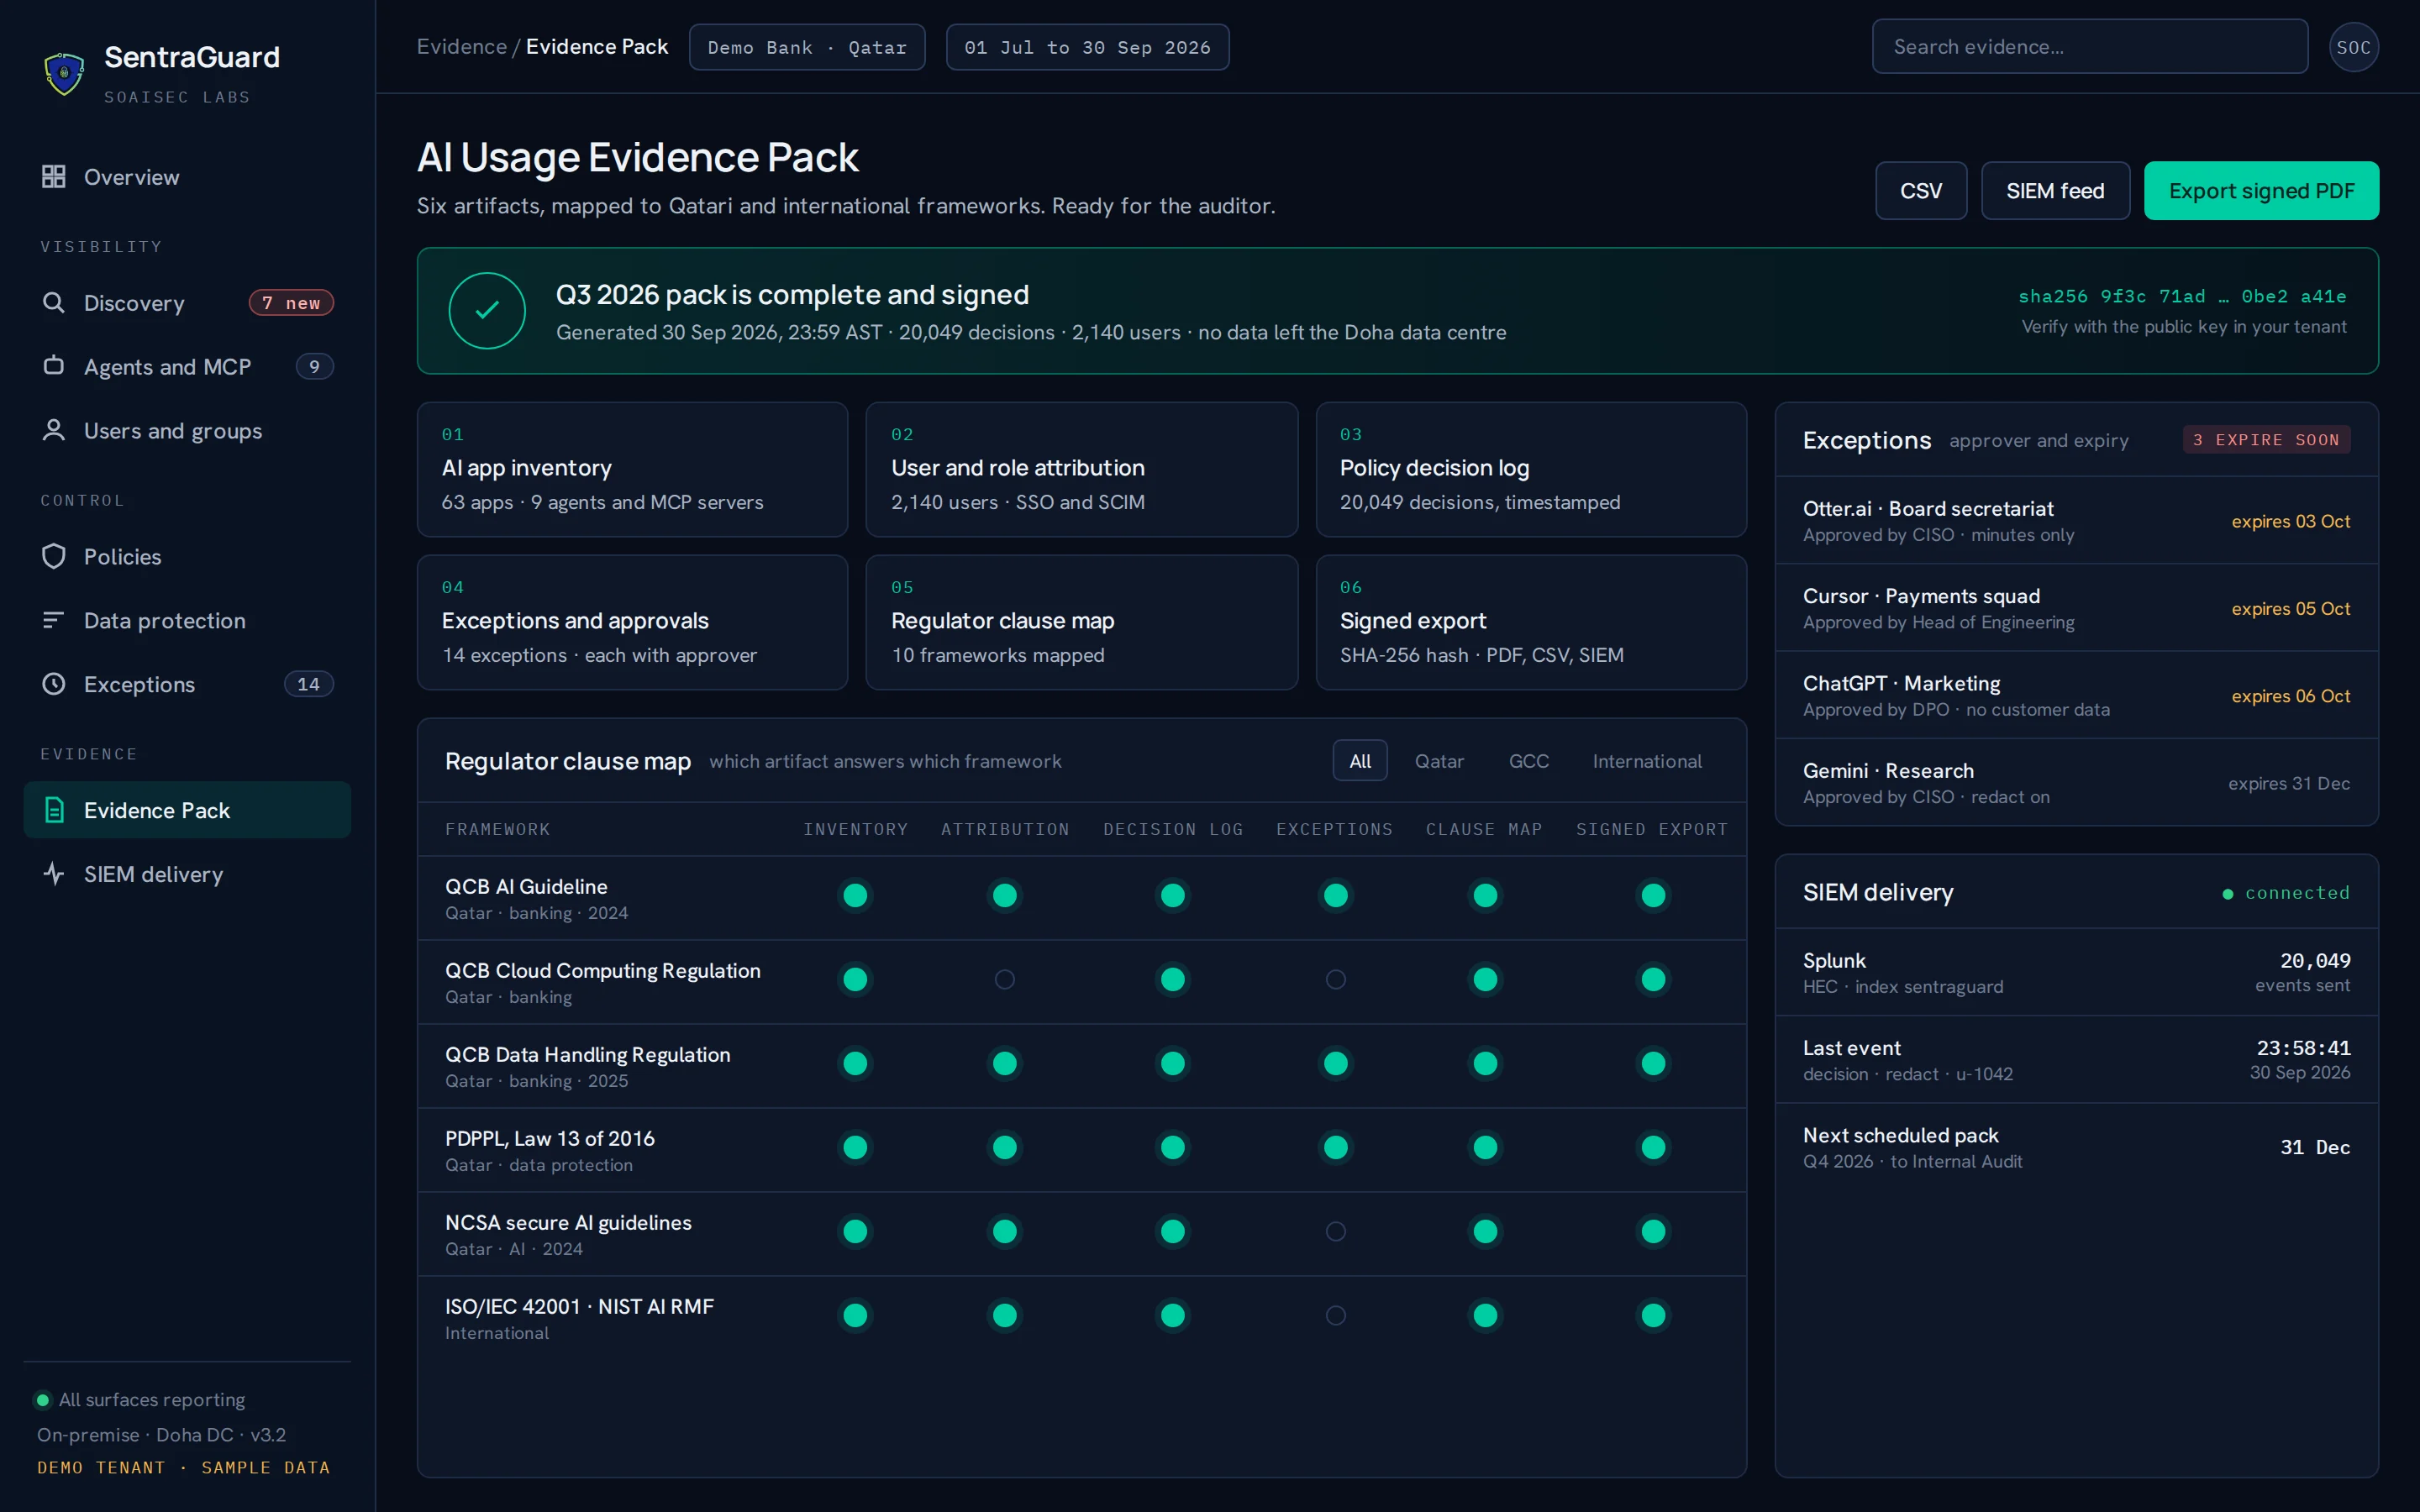
SentraGuard Discovery screen: 63 AI apps found, 41 used on personal accounts, 9 agents and MCP servers, with an app inventory by class and account type SentraGuard Data protection screen: live decision stream with Allow, Coach, Redact and Block, and an Emirates ID and IBAN redacted from a ChatGPT paste SentraGuard Evidence Pack screen: six signed artifacts and a clause map across QCB AI Guideline, QCB Cloud Computing Regulation, QCB Data Handling Regulation and ISO 42001
Product design · demo data
Open full size ↗

Four surfaces. One backend. Three outputs.

Every surface reports to the same API-first backend, so one policy applies everywhere and every event lands in the same log.

  • Asynchronous inspection, near real time
  • CPU only, no GPU, Kubernetes or VMs
  • Policy, SIEM feed and the Evidence Pack from one place
Four surfaces feed one SentraGuard backend, which outputs policy, SIEM events and the Evidence Pack Browser plugin IDE extension SDK and API gateway Endpoint agent SentraGuardbackend API-first · asynchronousCPU only · no GPUKubernetes · VM · air gapped Policy: four actions SIEMSplunk · QRadar · Sentinel · ArcSight AI Usage Evidence Pack
Control

Turn AI policy into decisions your users understand.

3app classes: sanctioned, tolerated, unsanctioned
4actions: allow, coach, redact, block
1policy, applied on every surface
Four rungs rising from Observe to Block; the pilot runs on Observe ObserveCoachRedactBlock log sessions,account, data class banner on IBAN,Emirates ID, Iqama strip identifiersbefore sending stop uploads totraining-by-defaulttools, prod writes USER IMPACT →CONTROL → THE PILOT RUNS HERE

Start in observe mode. Climb one rung at a time.

A bank can run the whole pilot on the first rung and see every session, account and data class with no user impact. Each rung above adds control for one app, one group or one data class at a time.

  • Observe: log and attribute, no message to the user
  • Coach: a banner with the approved path, session logged
  • Redact: the identifier is stripped, the prompt goes through
  • Block: stopped and logged, with the reason shown

Classify once. Decide per app, per group, per data class.

Mark each app sanctioned, tolerated or unsanctioned. New apps inherit their category's decision until you change it. Then set the action by user group and by the data class detected in the prompt.

  • Exceptions with an approver and an expiry date
  • Identity from SSO and SCIM, including personal accounts on corporate devices
  • Same rules for agents' tool calls
ApplicationRetail opsEngineeringContractors
ChatGPT Enterprisesanctioned · SSOAllowAllowRedact
ChatGPT personalunsanctionedCoachCoachBlock
Claude Codetolerated · engineeringBlockRedactBlock
DeepSeek webunsanctioned · trains by defaultBlockBlockBlock
M365 CopilotsanctionedAllowAllowCoach

Coach at the moment of use

A banner in the session, not a ticket the next day. The user sees why, what to do instead, and what is logged. Most usage moves to the approved tool without a block.

  • Gulf data classes: Emirates ID, Saudi National ID, Iqama, IBAN
  • Coach interactions double as AI literacy evidence
  • Redact strips the identifier and lets the prompt through
public AI assistant · corporate device · personal account
Summarise this customer's dispute. Emirates ID 784-1987-4521836-2, IBAN AE07 0331 2345 6789 0123 456, branch Deira, amount AED 84,200.
event: coach · data class: Emirates ID, IBAN · user: SSO-bound · surface: browser plugin · logged to SIEM
Policy decision preview

Pick an app, a data class and a user group. See what SentraGuard decides.

Illustrative rules. Your policy sets the real ones, per app, per group and per data class.

Every decision is logged with user, app, data class and action, and streamed to your SIEM.

Rung 2 of 4
Coach

Unsanctioned app on a personal account. The user sees the approved assistant and can continue; the session is logged.

What the user seesYou are using ChatGPT with a personal account. The approved assistant is one click away. Continue here if you must; this session is logged.
event: coach · app: ChatGPT (personal) · data: none · group: Retail operations · logged to SIEM
Protection

Stop sensitive data leaving in a prompt, a paste or a tool call.

4xrise in shadow AI detections in DLP data in one year. Verizon DBIR 2026
3lanes inspected before data leaves: prompt, paste, upload
0bytes sent to SOAISEC in on-premise and air-gapped deployments

Inspect the prompt, the paste and the upload before they leave

Detection runs on the session, on every surface, with the same data classes. Redact keeps the workflow moving. Block stops the ones that must not leave.

Emirates IDSaudi National ID and IqamaIBANCard number (PAN)Customer PIIMNPISource codeAPI keys and secretsInternal identifiersFile uploads by type
An agent with its identity, the tools and MCP servers it can call, and the data it can reach, each edge gated by SentraGuard AGENT TOOL-CALL CONTROL Agentowner · runtime · identity IdentitySSO-bound user Toolsshell · browser · HTTP MCP serversfiles · db · email Data storesCRM · core banking SGSGSG every call gated: allow, coach, redact or block
Evidence

Prove it to the regulator with a file, not a screenshot.

6artifacts in the AI Usage Evidence Pack
10frameworks mapped for Qatar and international standards
3formats: PDF, CSV, SIEM feed

The AI Usage Evidence Pack

Inventory, attribution, policy log, exceptions, a regulator clause map and a signed export. Produced from the same events the SIEM receives, so the auditor and the SOC read one truth.

PDFCSVSIEM feedSigned hash
AI Usage Evidence Pack · Q3 FY27 · [Institution]
Period01 Jul to 30 Sep 2026
Scope2,140 users · 4 surfaces
Apps discovered63 (41 with personal-account sessions)
Agents and MCP servers9 (4 with write access)
Decisions18,402 allow · 1,207 coach · 388 redact · 52 block
sha256: 3f1c…a9e2 · signed export · illustrative

The framework the auditor cites. The evidence that answers it.

Select a jurisdiction. Each dot is an artifact SentraGuard produces for that framework.

FrameworkInventoryAttributionPolicy logRedaction proofClause mapSigned export
QCB Artificial Intelligence Guideline (2024)
QCB Cloud Computing Regulation (2024)
QCB Data Handling and Protection Regulation (2025)
PDPPL, Law No. 13 of 2016
QFC Data Protection Regulations 2021
NCSA Guidelines for Secure Adoption and Usage of AI (2024)
NIA Standard and National Data Classification Policy
MCIT Principles and Guidelines for Ethical AI (2024)
evidence SentraGuard produces for this framework   not required
Details: what each framework expects
FrameworkWhat it expects
QCB Artificial Intelligence Guideline (2024)AI register with annual disclosure, prior approval, board accountability, human oversight, outsourcing approval
QCB Cloud Computing Regulation (2024)Risk-based cloud governance, lifecycle and security controls
QCB Data Handling and Protection Regulation (2025)Data classification, governance and security for QCB-licensed firms
PDPPL, Law No. 13 of 2016Special-nature data permits, breach notice; fines up to QAR 5 million
QFC Data Protection Regulations 2021Data protection in the QFC; 72-hour breach notice
NCSA Guidelines for Secure Adoption and Usage of AI (2024)Generative AI, privacy and governance
NIA Standard and National Data Classification PolicyInformation assurance and data classification for government and vital sectors
MCIT Principles and Guidelines for Ethical AI (2024)Non-binding principles for ethical AI
ISO/IEC 42001AI management system: inventory, roles, controls and monitoring for AI in use
NIST AI RMFGovern, Map, Measure, Manage
Seen enough to test it on your own staff?Find your shadow AI on the day you deploy. Reach full governance in one week, on one business unit.
Start a one-week pilot
Deployment

Runs where a regulated institution is allowed to run software.

SaaSHosted by SOAISEC
Private cloudYour AWS, Azure or Google Cloud tenant
On premiseKubernetes or VMs, CPU only
Air gappedNo outbound link, signed update bundles
FAQ

Questions a CISO asks first

Answers for Gulf banks, insurers and government entities.

Does it log prompts?

Observe records the app, the account type, the data class and the decision. Prompt text is captured only where a policy requires it, and it stays inside your deployment.

Does it govern AI agents and MCP servers?

Yes. The endpoint agent finds MCP servers, clients and CLI agents at runtime on Windows, macOS and Linux. The SDK and API gateway cover in-house agents. Tool calls get the same four actions as prompts.

Does it work air gapped?

Yes. Kubernetes or VMs with no outbound connection. The app dictionary and detection updates arrive as signed bundles.

Does it slow the browser?

Inspection is asynchronous and near real time. The measured p95 will be published after the first pilots, not before.

Does any data leave Qatar?

Not in the on-premise or air-gapped deployment. The backend runs in your data centre in Qatar on CPU only. Policy, logs and the Evidence Pack stay inside your perimeter, in line with QCB data handling rules and the national data classification policy.

How is it licensed?

Per protected user per year, by tier: Browser, Workforce, Enterprise. Quotes are issued at the pilot readout. There is no public price list.

Meet with us

Start a one-week pilot

Find your shadow AI on the day you deploy. Reach full shadow AI governance in one week, for one business unit. Delivered by the SOAISEC GCC team with Forcespot, our value-added distributor in the region, and NitronEdge, our value-added solution seller.

Day 0Deploy and discover. Plugin and endpoint agent pushed by Intune, Jamf or Google Admin. Your shadow AI inventory the same day: apps, personal accounts, agents and MCP servers.
Day 1 to 2Classify. Apps marked sanctioned, tolerated or unsanctioned. Sensitive data mapped by class and lane.
Day 3 to 4Coach and redact. Live for the pilot groups on QID, IBAN, card numbers and customer PII.
Day 5 to 6Block. Unsanctioned and training-by-default tools stopped. Exceptions with an approver and an expiry date.
Day 7Full governance. All four actions live, AI Usage Evidence Pack, executive readout and a quote priced from your pilot data.
Resources

Not ready for a pilot? Start here.

Guide

What is AI Usage Control? A guide for GCC banks, insurers and government

The category, the four decisions, what UAE and Saudi regulators expect, and a 12-question vendor checklist.

Read the guide
Buyer's guide

22 shadow AI platforms compared by surface, deployment and evidence

Filter by browser extension, endpoint agent, on premise and price. Compiled from public vendor sites.

Compare the platforms
Sample

AI Usage Evidence Pack, 12-page sample

Inventory, decisions, agents, exceptions, UAE and Saudi clause maps and a signed export. Printable.

Open the sample
Article

Why banning ChatGPT creates shadow AI in Gulf banks

Bans push usage to personal accounts. A one-week path from ban to governed use.

Read the article
Article

Shadow AI under Saudi PDPL and UAE PDPL

Eight questions the auditor will ask, and the evidence that answers each one.

Read the article
Video

SentraGuard in two minutes

Shadow AI found on day 0, an unsanctioned tool moved to sanctioned use, Microsoft 365 Copilot governed, and all four actions live by day 7. Voiceover, captions and transcript.

Watch the video