Guide
What is AI Usage Control? A guide for GCC banks, insurers and government
The category, the four decisions, what UAE and Saudi regulators expect, and a 12-question vendor checklist.
Read the guideStaff in Gulf banks, insurers and government use AI tools you cannot see, often on personal accounts, with customer data. SentraGuard finds every AI app, agent and account, governs each one, and proves it to your regulator.
Find your shadow AI on the day you deploy. Reach full shadow AI governance in one week.
 ISO 27001 CERTIFIED
Each Gulf market regulates AI and personal data in its own way. Pick yours to see the regulators, fines, data residency rules and identifiers that apply.
CBUAE AI guidance note (2026), DIFC Regulation 10, ADGM fines up to USD 28M.
See the UAE page Saudi ArabiaSDAIA confirmed 48 PDPL violations in 2025. New NCA AI guidelines.
See the KSA page OmanPDPL fully enforceable since 5 Feb 2026. Transfer fines up to OMR 500,000.
See the Oman page QatarQCB AI Guideline: register every AI system. PDPPL fines up to QAR 5M.
See the Qatar pageSensitive data does not leave through files any more. It leaves in a prompt, a paste and an agent's tool call, usually on a personal account. Usage control decides what happens at that moment.
67% of employees reach AI from non-corporate accounts on corporate devices. No log, no attribution, no answer for the auditor. Verizon DBIR 2026
Shadow AI is now the third most common non-malicious insider action in DLP data, with detections up 4x in a year. Source code is the top data type uploaded. Verizon DBIR 2026
Coding agents and MCP servers call tools and write to data. A tool list cannot govern a tool call.
Under Saudi PDPL, disclosing sensitive data can cost up to SAR 3 million and two years in prison; other violations up to SAR 5 million, doubled for repeat offenders. SDAIA began active enforcement in 2026. DLA Piper, PDPL
The session blind spot
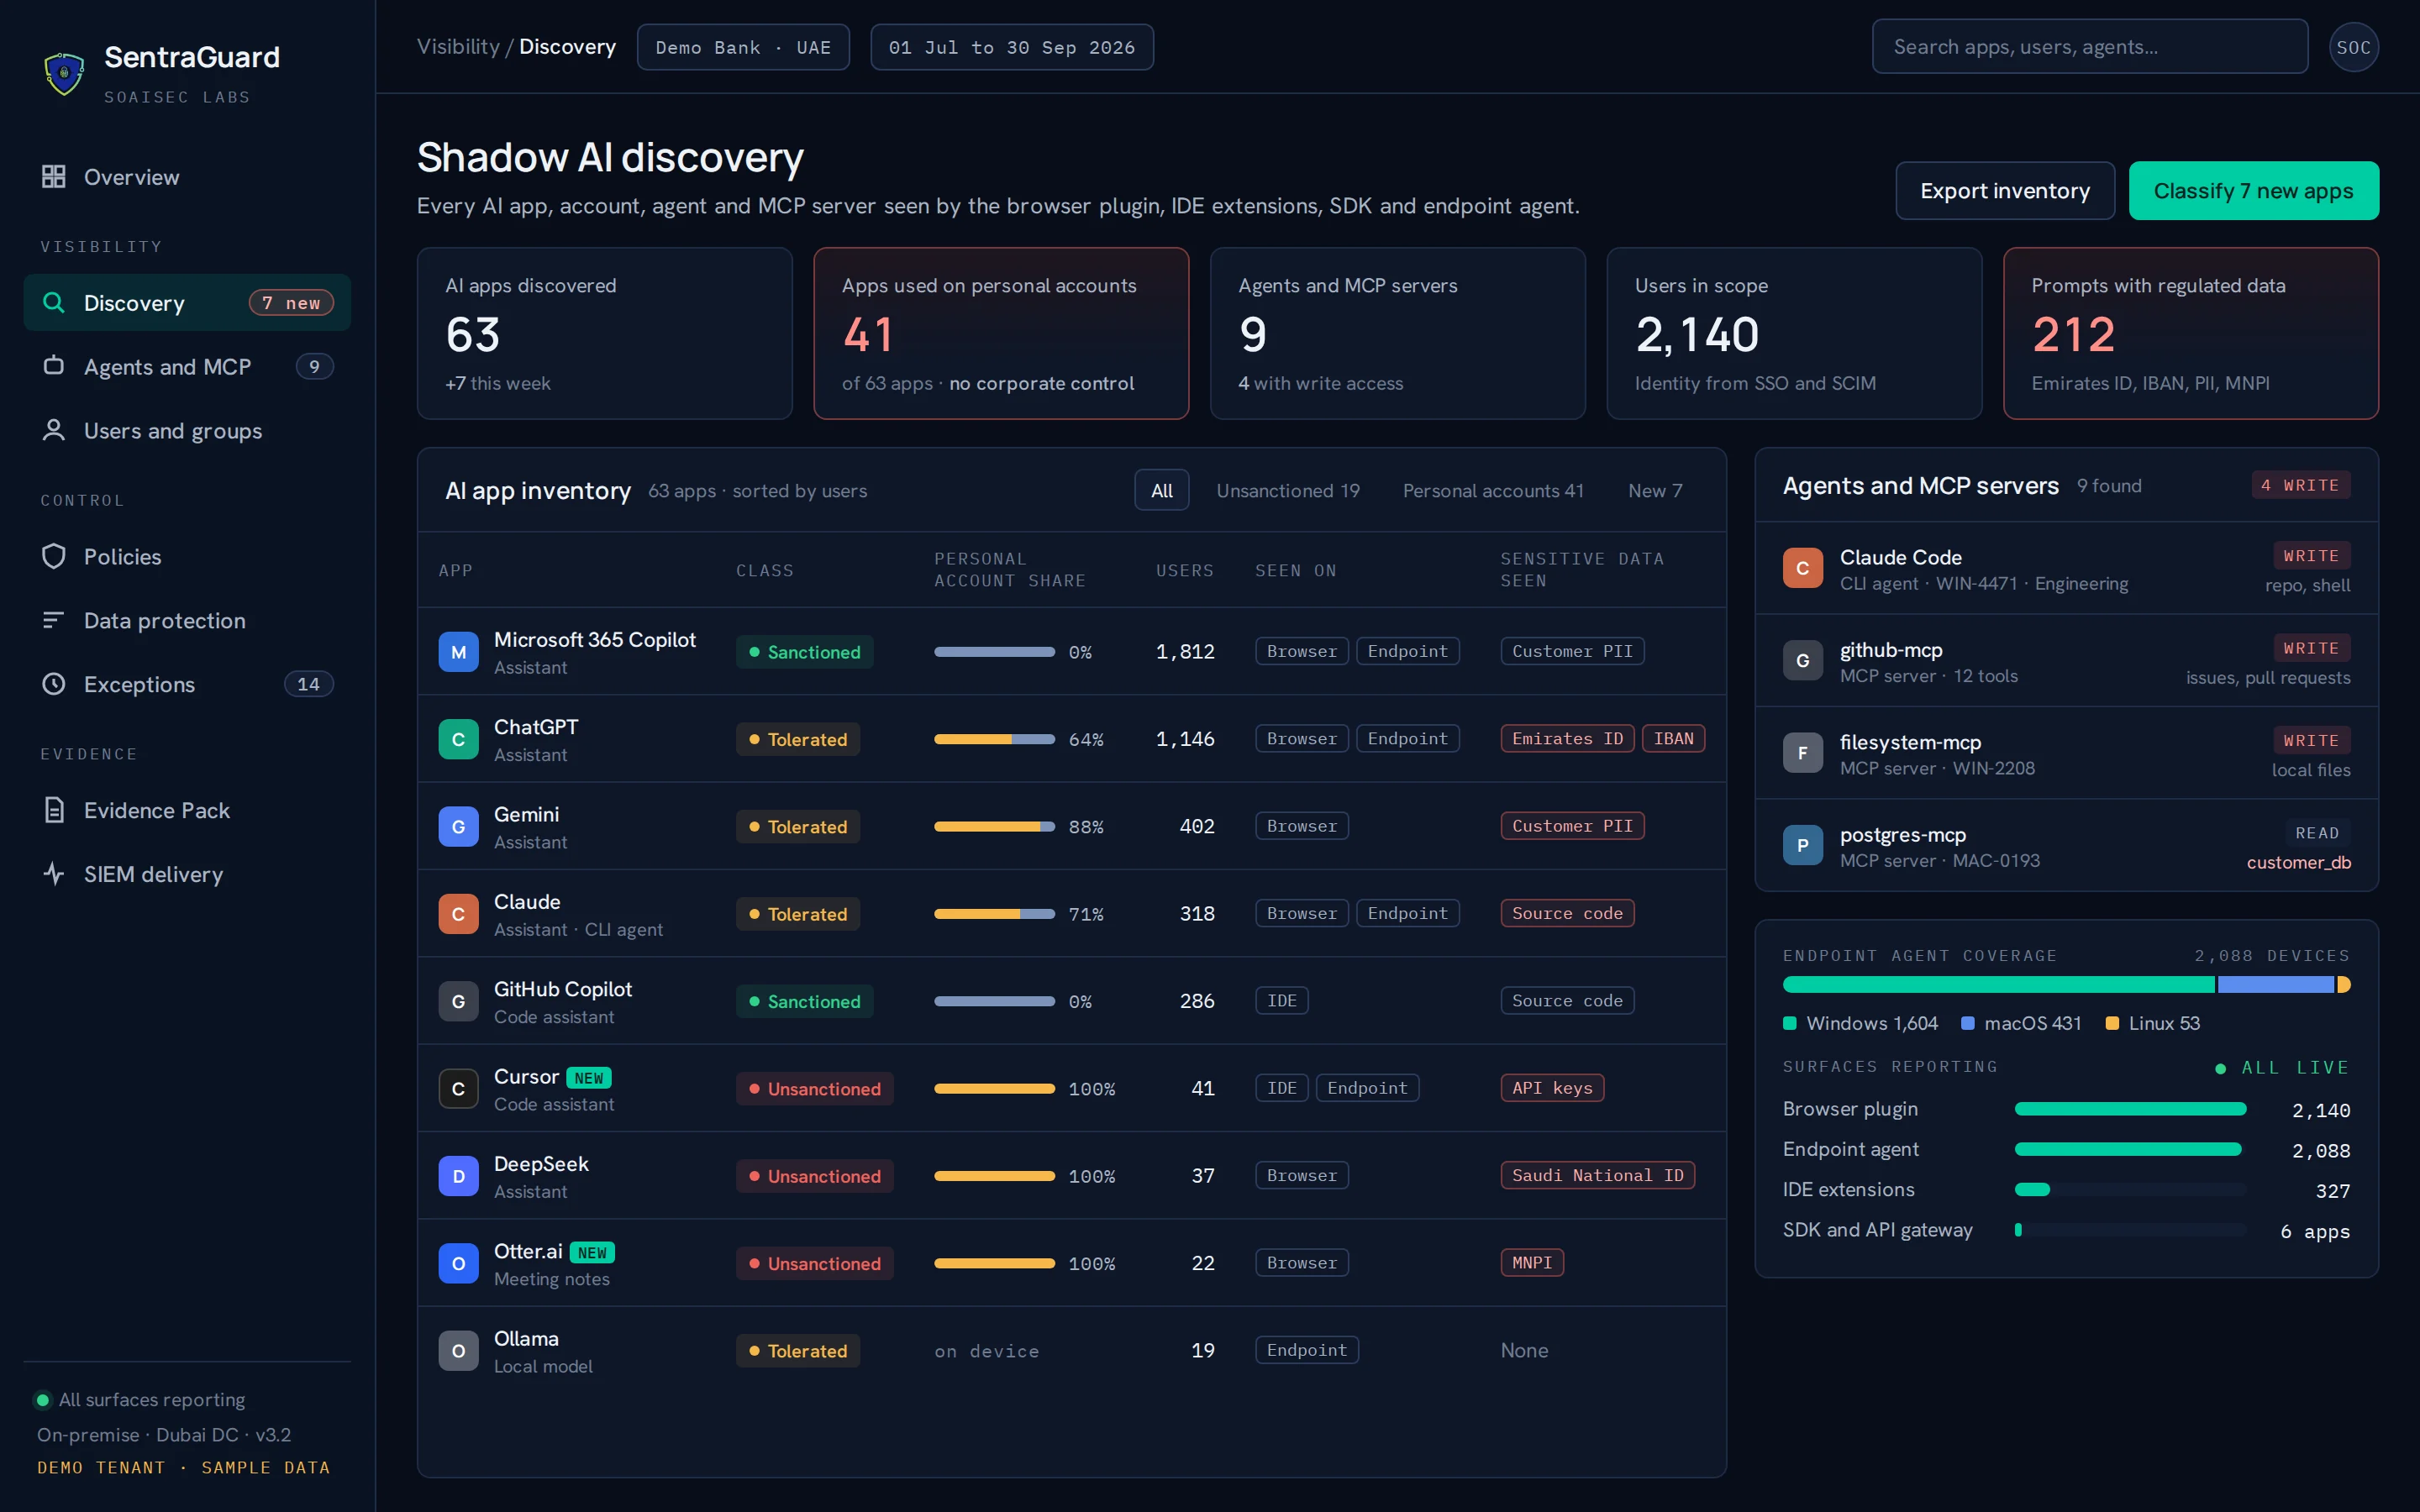
The browser plugin sees web apps and extensions. The IDE extension sees Cursor, VS Code and Copilot. The SDK and API gateway see your own apps. The endpoint agent runs on Windows, macOS and Linux and sees desktop AI apps, CLI agents, local models and MCP servers. Everything lands in one console.
Every surface reports to the same API-first backend, so one policy applies everywhere and every event lands in the same log.
A bank can run the whole pilot on the first rung and see every session, account and data class with no user impact. Each rung above adds control for one app, one group or one data class at a time.
Mark each app sanctioned, tolerated or unsanctioned. New apps inherit their category's decision until you change it. Then set the action by user group and by the data class detected in the prompt.
| Application | Retail ops | Engineering | Contractors |
|---|---|---|---|
| ChatGPT Enterprisesanctioned · SSO | Allow | Allow | Redact |
| ChatGPT personalunsanctioned | Coach | Coach | Block |
| Claude Codetolerated · engineering | Block | Redact | Block |
| DeepSeek webunsanctioned · trains by default | Block | Block | Block |
| M365 Copilotsanctioned | Allow | Allow | Coach |
A banner in the session, not a ticket the next day. The user sees why, what to do instead, and what is logged. Most usage moves to the approved tool without a block.
Illustrative rules. Your policy sets the real ones, per app, per group and per data class.
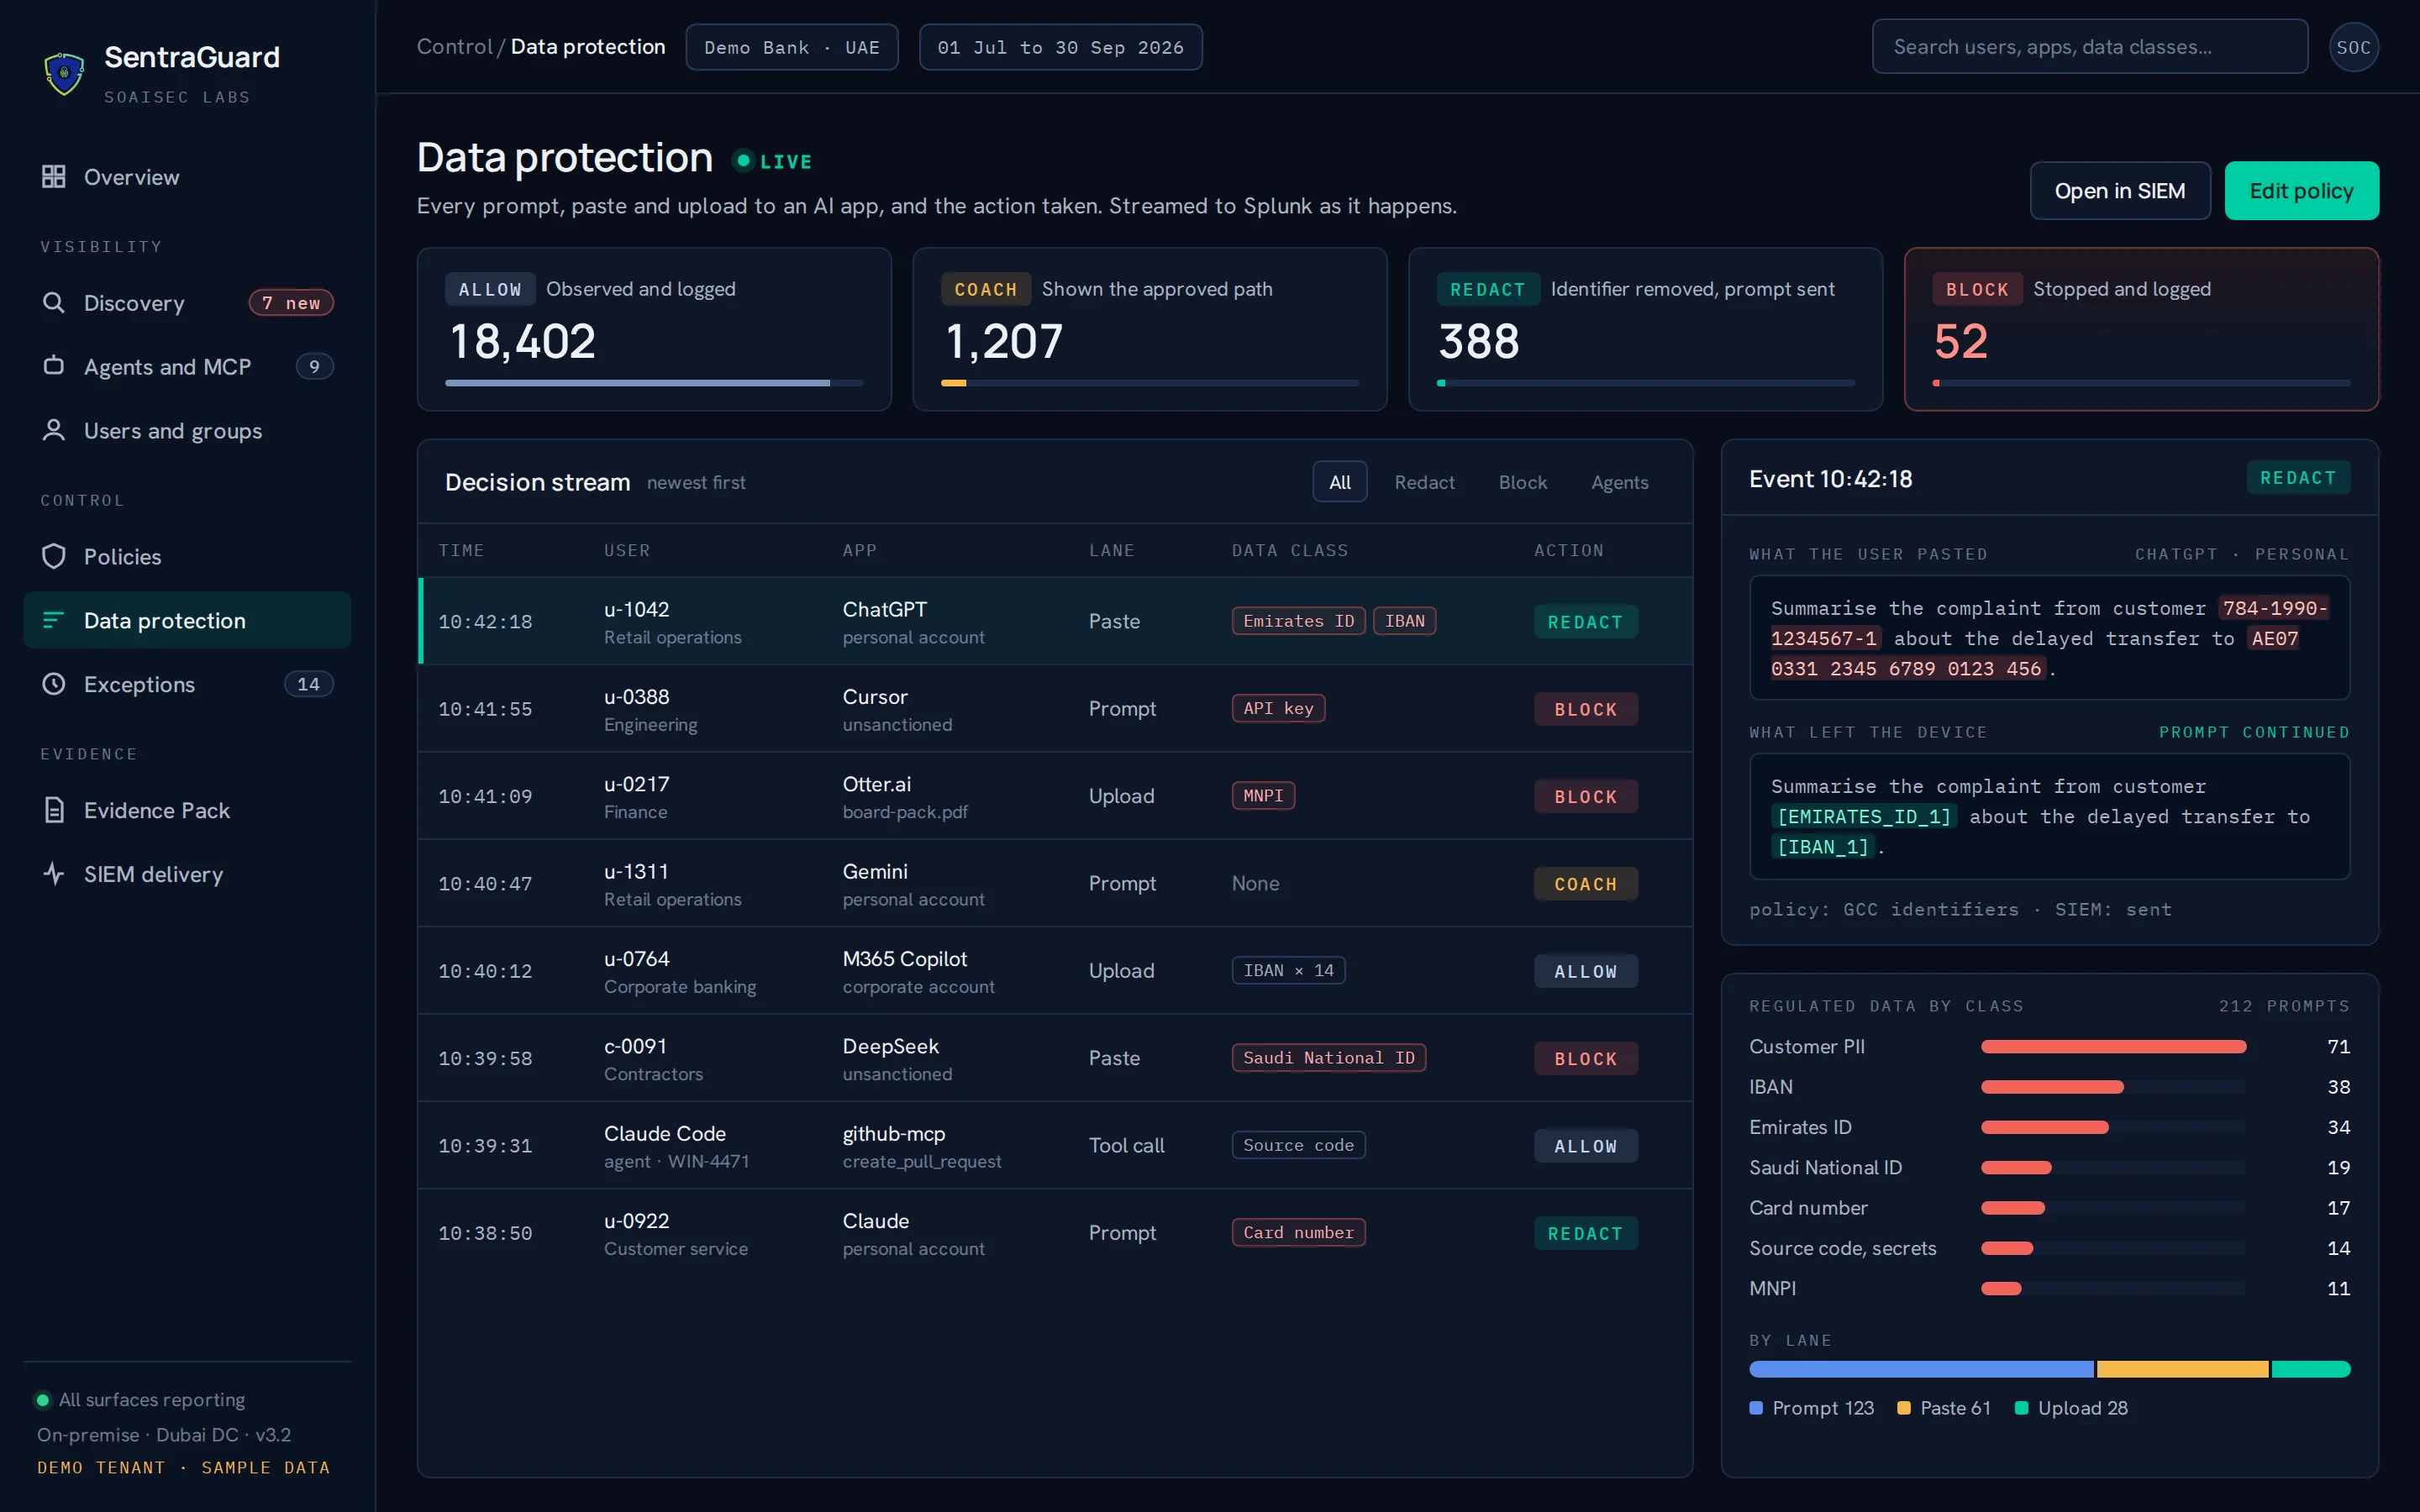
Every decision is logged with user, app, data class and action, and streamed to your SIEM.
Unsanctioned app on a personal account. The user sees the approved assistant and can continue; the session is logged.
Detection runs on the session, on every surface, with the same data classes. Redact keeps the workflow moving. Block stops the ones that must not leave.
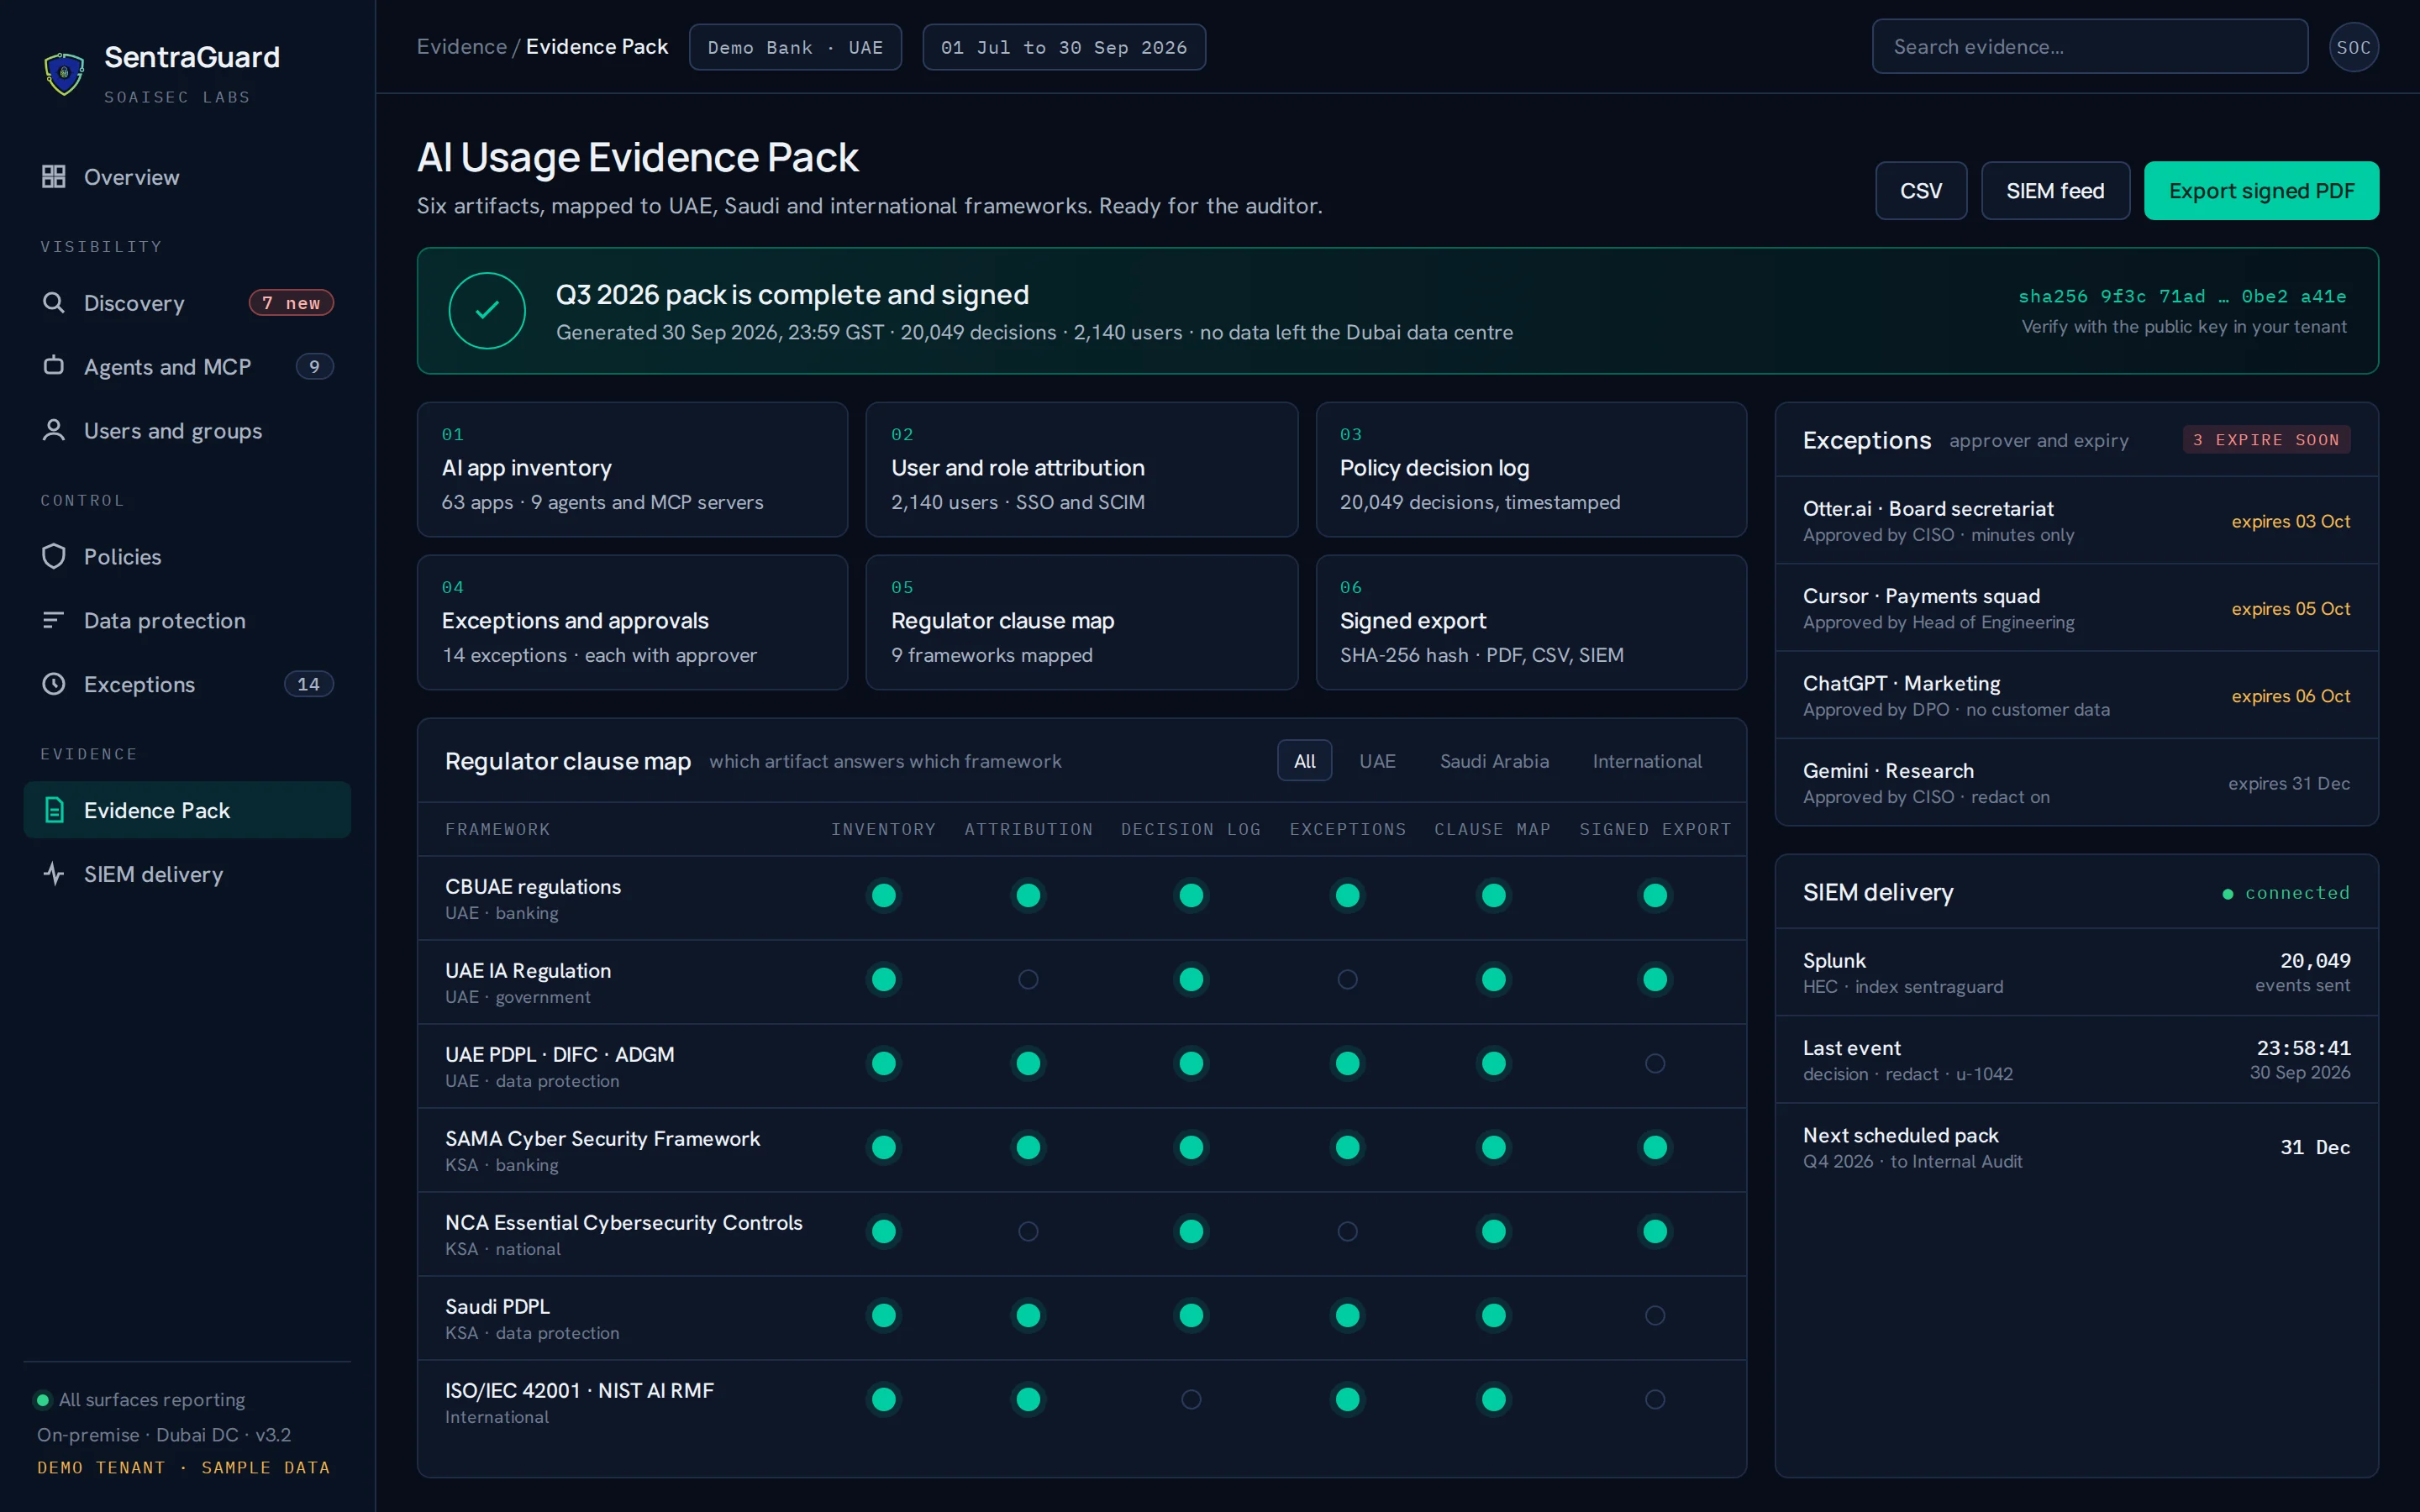
Inventory, attribution, policy log, exceptions, a regulator clause map and a signed export. Produced from the same events the SIEM receives, so the auditor and the SOC read one truth.
Select a jurisdiction. Each dot is an artifact SentraGuard produces for that framework.
| Framework | Inventory | Attribution | Policy log | Redaction proof | Clause map | Signed export |
|---|---|---|---|---|---|---|
| CBUAE guidance note on AI and ML (2026) | ||||||
| Central Bank Law, Decree-Law 6 of 2025 | ||||||
| CBUAE Consumer Protection Regulation and Standards | ||||||
| CBUAE Outsourcing Regulation for Banks (2021) | ||||||
| UAE Information Assurance Regulation and IA Standard v2 | ||||||
| UAE PDPL, Decree-Law 45 of 2021 | ||||||
| DIFC Data Protection Law 2020 and Regulation 10 | ||||||
| ADGM Data Protection Regulations 2021 | ||||||
| Dubai DESC Information Security Regulation | ||||||
| UAE Charter for the Development and Use of AI (2024) |
| Framework | Inventory | Attribution | Policy log | Redaction proof | Clause map | Signed export |
|---|---|---|---|---|---|---|
| SAMA Cyber Security Framework | ||||||
| NCA Essential Cybersecurity Controls, ECC-2:2024 | ||||||
| NCA Cloud Cybersecurity Controls, CCC-2:2024 | ||||||
| NCA Data Cybersecurity Controls, DCC-1:2022 | ||||||
| NCA AI Cybersecurity Guidelines (draft, 2026) | ||||||
| PDPL, Royal Decree M/19, and its regulations | ||||||
| SDAIA Generative AI Guidelines (2024) | ||||||
| SDAIA AI Ethics Principles (2023) |
| Framework | Inventory | Attribution | Policy log | Redaction proof | Clause map | Signed export |
|---|---|---|---|---|---|---|
| PDPL, Royal Decree 6/2022, and Executive Regulations 34/2024 | ||||||
| MTCIT Cloud and Hosting Services Standard | ||||||
| Cloud Computing First Circular 10/2026 | ||||||
| National Data Governance framework and Data Classification Policy | ||||||
| CBO Cyber Security and Resilience Framework (2023) | ||||||
| Oman CERT Basic Security Controls | ||||||
| MTCIT Public Policy for the Safe and Ethical Use of AI Systems (2025) |
| Framework | Inventory | Attribution | Policy log | Redaction proof | Clause map | Signed export |
|---|---|---|---|---|---|---|
| QCB Artificial Intelligence Guideline (2024) | ||||||
| QCB Cloud Computing Regulation (2024) | ||||||
| QCB Data Handling and Protection Regulation (2025) | ||||||
| PDPPL, Law No. 13 of 2016 | ||||||
| QFC Data Protection Regulations 2021 | ||||||
| NCSA Guidelines for Secure Adoption and Usage of AI (2024) | ||||||
| NIA Standard and National Data Classification Policy | ||||||
| MCIT Principles and Guidelines for Ethical AI (2024) |
| Framework | Inventory | Attribution | Policy log | Redaction proof | Clause map | Signed export |
|---|---|---|---|---|---|---|
| ISO/IEC 42001 | ||||||
| NIST AI RMF |
| Framework | What it expects |
|---|---|
| CBUAE guidance note on AI and ML (2026) | Generative AI, data privacy, third-party and outsourced AI, consumer protection |
| Central Bank Law, Decree-Law 6 of 2025 | New law for licensed financial institutions; compliance by 16 Sep 2026; fines up to AED 1 billion |
| CBUAE Consumer Protection Regulation and Standards | Customer data protection for licensed financial institutions |
| CBUAE Outsourcing Regulation for Banks (2021) | Third-party and outsourcing controls |
| UAE Information Assurance Regulation and IA Standard v2 | Asset inventory, data classification, monitoring and logging |
| UAE PDPL, Decree-Law 45 of 2021 | Lawful processing and cross-border transfer; executive regulations pending |
| DIFC Data Protection Law 2020 and Regulation 10 | Register of AI use cases, human review, Autonomous Systems Officer |
| ADGM Data Protection Regulations 2021 | Breach report within 72 hours; fines up to USD 28 million |
| Dubai DESC Information Security Regulation | Information security for Dubai Government entities |
| UAE Charter for the Development and Use of AI (2024) | Twelve principles, including privacy, human oversight and accountability |
| SAMA Cyber Security Framework | Third-party security, outsourcing and cloud; SAMA approval for material outsourcing |
| NCA Essential Cybersecurity Controls, ECC-2:2024 | Asset management, event logging, external and cloud services; data localisation |
| NCA Cloud Cybersecurity Controls, CCC-2:2024 | Cloud controls updated for data localisation |
| NCA Data Cybersecurity Controls, DCC-1:2022 | Controls across the data lifecycle |
| NCA AI Cybersecurity Guidelines (draft, 2026) | Governance, defence, resilience and third-party controls for generative and agentic AI |
| PDPL, Royal Decree M/19, and its regulations | Processing rules, Transfer Regulations, 72-hour breach notice; fines up to SAR 5 million |
| SDAIA Generative AI Guidelines (2024) | Responsible use of generative AI by government and the public |
| SDAIA AI Ethics Principles (2023) | Accountability, privacy and transparency for AI in use |
| PDPL, Royal Decree 6/2022, and Executive Regulations 34/2024 | Transfer rules, sensitive data permits, DPO, 72-hour breach notice; fines up to OMR 500,000 |
| MTCIT Cloud and Hosting Services Standard | Government data hosted and processed only within Oman, including backup |
| Cloud Computing First Circular 10/2026 | Classify data before it moves to the cloud |
| National Data Governance framework and Data Classification Policy | Data classification and governance across government |
| CBO Cyber Security and Resilience Framework (2023) | Cyber resilience and third-party risk for banks and payment firms |
| Oman CERT Basic Security Controls | Baseline security controls for government bodies |
| MTCIT Public Policy for the Safe and Ethical Use of AI Systems (2025) | Safe and ethical AI use in the public and private sectors |
| QCB Artificial Intelligence Guideline (2024) | AI register with annual disclosure, prior approval, board accountability, human oversight, outsourcing approval |
| QCB Cloud Computing Regulation (2024) | Risk-based cloud governance, lifecycle and security controls |
| QCB Data Handling and Protection Regulation (2025) | Data classification, governance and security for QCB-licensed firms |
| PDPPL, Law No. 13 of 2016 | Special-nature data permits, breach notice; fines up to QAR 5 million |
| QFC Data Protection Regulations 2021 | Data protection in the QFC; 72-hour breach notice |
| NCSA Guidelines for Secure Adoption and Usage of AI (2024) | Generative AI, privacy and governance |
| NIA Standard and National Data Classification Policy | Information assurance and data classification for government and vital sectors |
| MCIT Principles and Guidelines for Ethical AI (2024) | Non-binding principles for ethical AI |
| ISO/IEC 42001 | AI management system: inventory, roles, controls and monitoring for AI in use |
| NIST AI RMF | Govern, Map, Measure, Manage |
Answers for Gulf banks, insurers and government entities.
Observe records the app, the account type, the data class and the decision. Prompt text is captured only where a policy requires it, and it stays inside your deployment.
Yes. The endpoint agent finds MCP servers, clients and CLI agents at runtime on Windows, macOS and Linux. The SDK and API gateway cover in-house agents. Tool calls get the same four actions as prompts.
Yes. Kubernetes or VMs with no outbound connection. The app dictionary and detection updates arrive as signed bundles.
Inspection is asynchronous and near real time. The measured p95 will be published after the first pilots, not before.
Not in the on-premise or air-gapped deployment. The backend runs in your own data centre on CPU only, whether that is in the UAE, Saudi Arabia, Oman or Qatar. Policy, logs and the Evidence Pack stay inside your perimeter. Each country page lists the residency rules that apply.
Per protected user per year, by tier: Browser, Workforce, Enterprise. Quotes are issued at the pilot readout. There is no public price list.
Find your shadow AI on the day you deploy. Reach full shadow AI governance in one week, for one business unit. Delivered by the SOAISEC GCC team with Forcespot, our value-added distributor in the region, and NitronEdge, our value-added solution seller.
The category, the four decisions, what UAE and Saudi regulators expect, and a 12-question vendor checklist.
Read the guideFilter by browser extension, endpoint agent, on premise and price. Compiled from public vendor sites.
Compare the platformsInventory, decisions, agents, exceptions, UAE and Saudi clause maps and a signed export. Printable.
Open the sampleBans push usage to personal accounts. A one-week path from ban to governed use.
Read the articleEight questions the auditor will ask, and the evidence that answers each one.
Read the articleShadow AI found on day 0, an unsanctioned tool moved to sanctioned use, Microsoft 365 Copilot governed, and all four actions live by day 7. Voiceover, captions and transcript.
Watch the video